> ## Documentation Index
> Fetch the complete documentation index at: https://docs.airmdr.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Google Cloud Platform - Security Command Center
> Security Command Center (SCC) is Google Cloud’s centralized security and risk management platform. It helps detect, investigate, and remediate security threats, vulnerabilities, and misconfigurations across Google Cloud resources.
### Purpose
The Google Cloud Platform integration connects AirMDR to Google Cloud APIs by using a dedicated service account.
After the connection is configured, AirMDR can retrieve supported security and operational information from the selected Google Cloud organization and projects.
AirMDR provides two configuration methods:
| Setup method | Description | Recommended for |
| :- | :- | :- |
| [**Use a Script**](https://docs.airmdr.com/Integrations/GCP-SCC#method-1-use-a-script-setup-steps) | Generates a Python script that automates service-account creation and related configuration steps. | New integrations and users who want a simplified setup |
| [**Do It Yourself**](https://docs.airmdr.com/Integrations/GCP-SCC#method-2-do-it-yourself-setup-steps) | Requires the administrator to manually create the service account, assign IAM roles, and generate the JSON key. | Organizations that require manual review and execution of every configuration step |
**Recommended:** Use the "**[Use a Script](https://docs.airmdr.com/Integrations/GCP-SCC#method-1-use-a-script-setup-steps)"** method to reduce manual configuration. Use **Do It Yourself** when your organization requires changes to be performed manually through the Google Cloud Console.
### Pre-requisites
User Organization must define **Owner** or **Security Admin** role (`roles/owner` or `roles/securitycenter.admin`) in your GCP organization.
User must have **Organization Admin** permissions to enable services at the organization level.
1. Select your organization, and enter keyword "Security" in the search bar.
2. Select the **Security Command Center**.
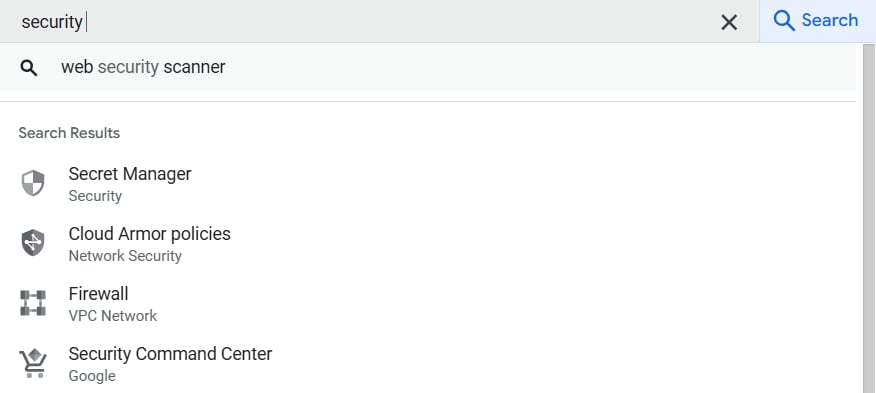 3. Click on "**GET THE SECURITY COMMAND CENTER**".
4. Make sure Service Tier is **Premium (Paid)** for your organization.
**SCC Editions: Standard vs. Premium Feature support (For reference)**
| Feature | Standard (Free) | Premium (Paid) |
| :- | :- | :- |
| Security Health Analytics | ✅ Basic | ✅ Advanced |
| Event Threat Detection | ❌ No | ✅ Yes |
| Container & VM Threat Detection | ❌ No | ✅ Yes |
| Continuous Compliance Monitoring | ❌ No | ✅ Yes |
| Automated Security Insights | ❌ No | ✅ Yes |
AirMDR uses a Google Cloud service account JSON key to authenticate with Security Command Center.
### Required Authentication Details
| AirMDR field | Required | What to enter | Where to get it |
| :- | -: | :- | :- |
| `Service_account_json` | Yes | Complete JSON credentials generated for the AirMDR service account | Generated by the script or downloaded from **IAM & Admin → Service Accounts → Keys** |
| `Organization_id` | Yes | Numeric Google Cloud Organization ID | Google Cloud organization settings |
| `Project_id` | During script generation | Unique textual ID of the project in which the service account will be created | Google Cloud project settings or project selector |
| `Service_account_id` | Optional during script generation | Unique ID for the AirMDR service account | Enter a preferred value or use the value recommended by AirMDR |
The `Service_account_json` field must contain the complete JSON object, not only the service-account email or key ID.
```text theme={null}
"type": "service_account",
"project_id": "example-project-id",
"private_key_id": "REDACTED",
"private_key": "-----BEGIN PRIVATE KEY-----\nREDACTED\n-----END PRIVATE KEY-----\n",
"client_email": "airmdr-integration-gcp@example-project-id.iam.gserviceaccount.com",
"client_id": "REDACTED",
"token_uri": "https://oauth2.googleapis.com/token"
```
Never use actual service-account credentials in documentation, screenshots, tickets, email, chat, or source-code repositories.
### Runtime access model
The AirMDR service account uses read-only permissions for the currently documented skills. It does not require permission to modify Google Cloud resources.
The script performs temporary read/write setup actions because it creates the service account, assigns roles, enables services where applicable, and generates a service-account key.
The service account must have permission to read Security Command Center findings from the target organization.
Recommended minimum role:
| Role | Purpose |
| :- | :- |
| Security Center Findings Viewer | Allows the service account to retrieve Security Command Center findings. |
Additional roles may be required depending on the customer’s GCP hierarchy, organization policies, and AirMDR use case.
Use least-privilege access. Assign only the permissions required for AirMDR to retrieve Security Command Center findings.
The following permissions are required only by the administrator running the script or completing the manual setup. They are not runtime permissions for the AirMDR service account.
| Setup activity | Example Google Cloud role | Scope | Access type |
| - | - | - | - |
| Enable required APIs | Service Usage Admin (`roles/serviceusage.serviceUsageAdmin`) | Integration project | Read/Write |
| Create the service account | Service Account Admin (`roles/iam.serviceAccountAdmin`) | Integration project | Read/Write |
| Create the JSON key | Service Account Key Admin (`roles/iam.serviceAccountKeyAdmin`) | Service account or project | Read/Write |
| Grant organization-level IAM roles | Organization Administrator (`roles/resourcemanager.organizationAdmin`) | Organization | Read/Write |
| Configure Security Command Center, if required | Security Center Admin (`roles/securitycenter.admin`) | Organization | Read/Write |
| Component | Supported Details |
| :- | :- |
| Cloud Platform | Google Cloud Platform |
| Security Product | Google Cloud Security Command Center |
| Authentication Method | Service Account JSON |
| Required Identifier | Organization ID |
| AirMDR Configuration Type | Cloud API-based integration |
| API Used | Security Command Center API |
| Base Endpoint | `https://console.cloud.google.com` |
### Method 1: Use a Script Setup Steps
Use this method to automate the service-account and IAM configuration steps.
The Organization ID already exists in Google Cloud and must be entered before the script is generated.
1. Sign in to the [Google Cloud Console](https://console.cloud.google.com/).
2. Open the project selector in the top navigation bar.
3. Select the required organization.
4. Open the organization settings or **Manage resources** page.
5. Locate **Organization ID**.
6. Copy the numeric value.
Do not enter the organization name, domain, project name, or project number in the `Organization_id` field.
1. Sign in to [AirMDR](https://app.airmdr.com/).
2. In the left navigation pane, select **Integrations**.
3. Search for **Google Cloud Provider**.
4. Open the integration.
5. Select the **Connections** tab.
6. Click **+ Create**.
7. Enter a unique instance name.
Example: `example-org-gcp`
8. Select **Use a Script**.
1. Under **Select the script language you want to use**, select **Python** or **Terraform**.
2. Enter the following information:
| Field | Value |
| - | - |
| `Organization_id` | Numeric Google Cloud Organization ID |
| `Project_id` | Project ID in which the AirMDR service account will be created |
| `Service_account_id` | Optional preferred service-account ID, such as `airmdr-integration-gcp` |
3. Review the entered Organization ID and Project ID.
4. Click the **Download** icon.
The selected script (Python or Terraform) is downloaded to your computer.
> **Security recommendation:** Review the downloaded script before running it. Confirm that the organization, project, service-account ID, APIs, and IAM roles match the approved configuration.
1. Open [Google Cloud Shell](https://shell.cloud.google.com/).
2. Confirm that you are signed in with the approved Google Cloud administrator account.
3. Verify that the correct project is active.
You can optionally check the active project by running: `gcloud config get-value project`
Upload the downloaded script by using one of the following methods:
* Drag the file from your computer and drop it into the Cloud Shell terminal window.
(**OR)**
* Select the **three-dot menu** at the top of the Cloud Shell pane, and then select **Upload**.
The uploaded file is placed in the Cloud Shell home directory.
Confirm that the file is available:
```text theme={null}
ls -l
```
Run the uploaded Python script:
```text theme={null}
python3 script.py
```
If the downloaded file has a different name, replace `script.py` with the actual filename:
```text theme={null}
python3 .py
```
The account running the script must have permission to perform every operation included in the script. Using a script reduces manual steps but does not remove Google Cloud permission requirements.
After the script completes:
1. Confirm that it reports successful service-account creation and IAM role assignment.
2. Copy the `Service_account_json` generated by the script.
3. Copy or confirm the `Organization_id` shown in the output.
4. Do not close the terminal until the required values have been entered in AirMDR.
The Organization ID is not newly generated. The script returns or confirms the Organization ID supplied during script creation.
1. Return to the AirMDR connection form.
2. In `Service_account_json`, paste the complete JSON credentials generated by the script.
3. In `Organization_id`, enter the numeric Organization ID.
4. Expand **Advanced Configuration** only if additional settings are required.
5. Click **Save**.
6. Validate the connection.
### Method 2: Do It Yourself Setup Steps
This section explains how to collect the two required values for AirMDR:
* `service_account_json`
* `organization_id`
1. Sign in to the [Google Cloud Console](https://console.cloud.google.com/welcome).
2. In the ribbon, click on your project name.
3. From the top project selector, select the project that will be used for the AirMDR integration.
Confirm that you are working under the correct organization and project.
The selected project is where the service account and API configuration will be managed.
1. In [Google Cloud Console](https://console.cloud.google.com/welcome), open the navigation menu.
2. Go to **APIs & Services**.
3. Select **Library**.
4. Search for **Security Command Center API**.
5. Open the API page.
6. Click **Enable**.
1. In [Google Cloud Console](https://console.cloud.google.com/welcome), open the navigation menu.
2. Go to **IAM & Admin**.
3. Select **Service Accounts**.
4. Click **Create Service Account**.
5. Enter the following details:
| Field | Example Value | Description |
| :- | :- | :- |
| Service account name | `airmdr-integration-gcp` | Display name for the service account. |
| Service account ID | `airmdr-integration-gcp` | Unique ID generated for the service account. |
| Description | `Service account for AirMDR GCP SCC integration` | Optional description for tracking usage. |
6. Click **Create and Continue**.
7. Skip role assignment (Permissions and Principals with access) at this step if the role will be assigned at the organization level.
8. Click **Done**.
1. Search the service account created for AirMDR.
For example: `airmdr-integration-gcp`(as shown)
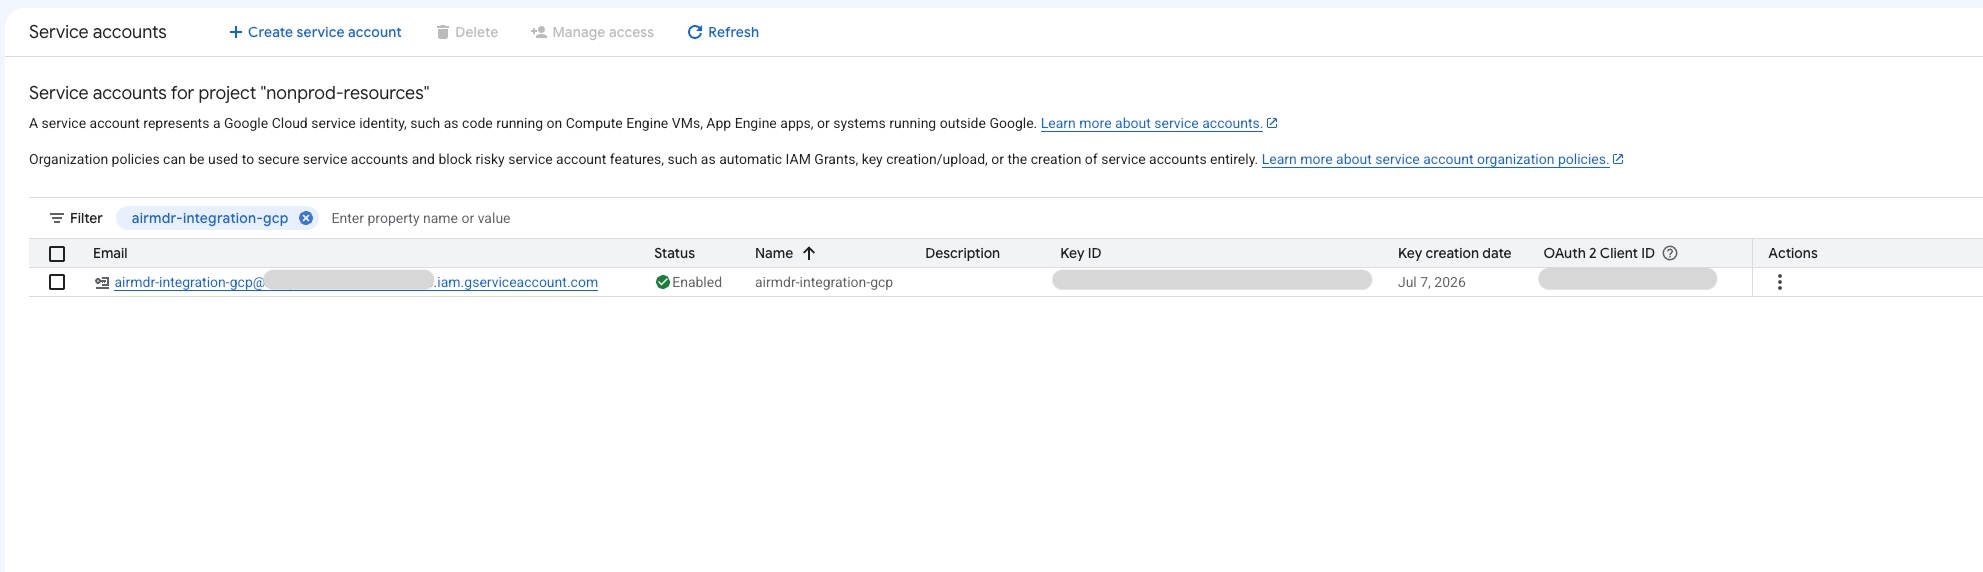 2. Open the **Keys** tab.
3. Click **Add Key** drop-down.
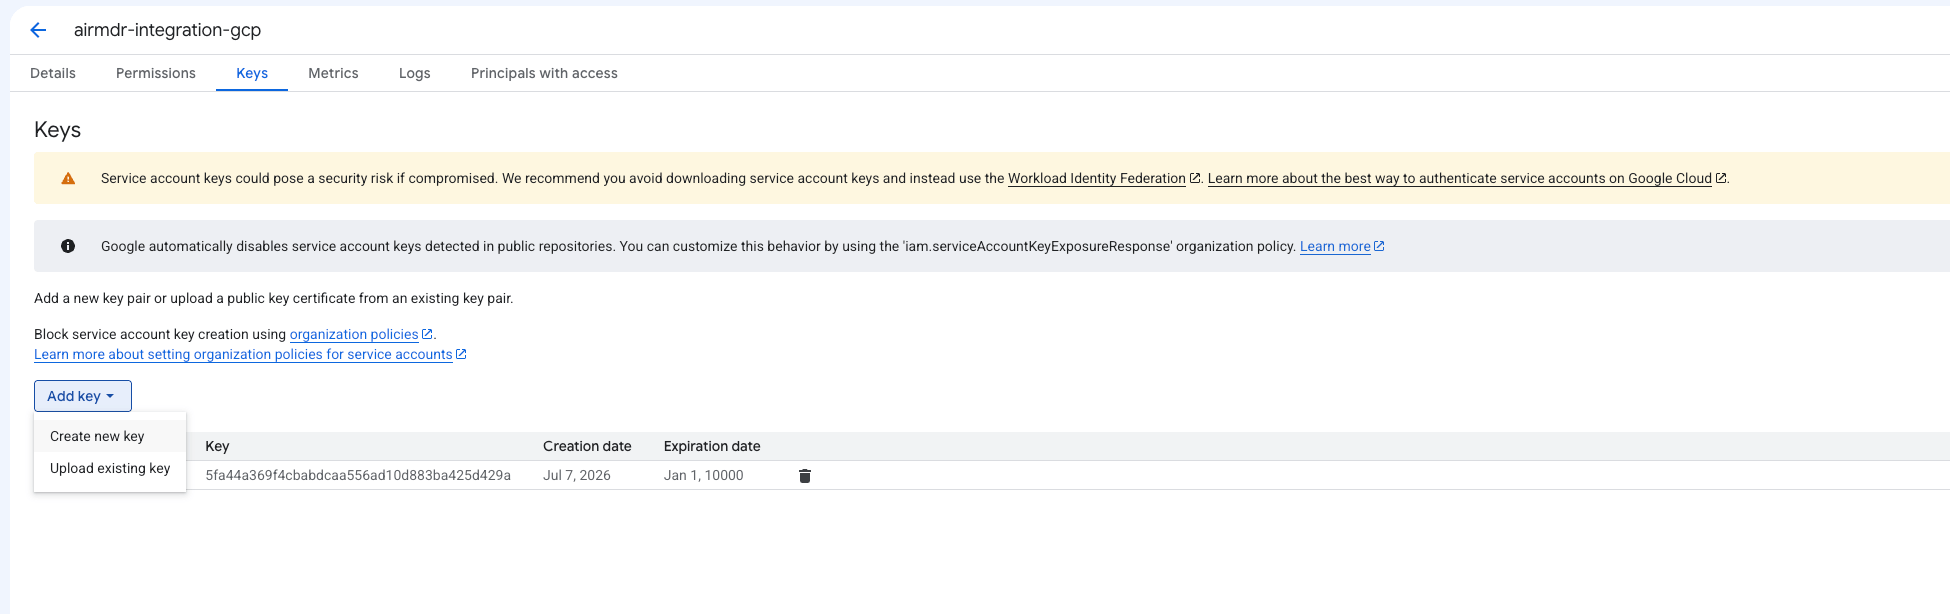 4. Select **Create new key**.
5. Select **JSON** as the key type.
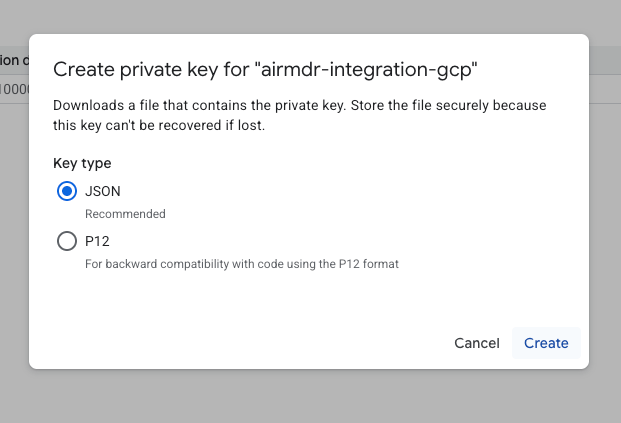 6. Click **Create**.
Permission updates for service accounts may take a few minutes to propagate. If access is not granted immediately, wait a few minutes and try again.
7. The JSON file is downloaded automatically.
The downloaded file is the `service_account_json` required in AirMDR.
**Example JSON Structure:**
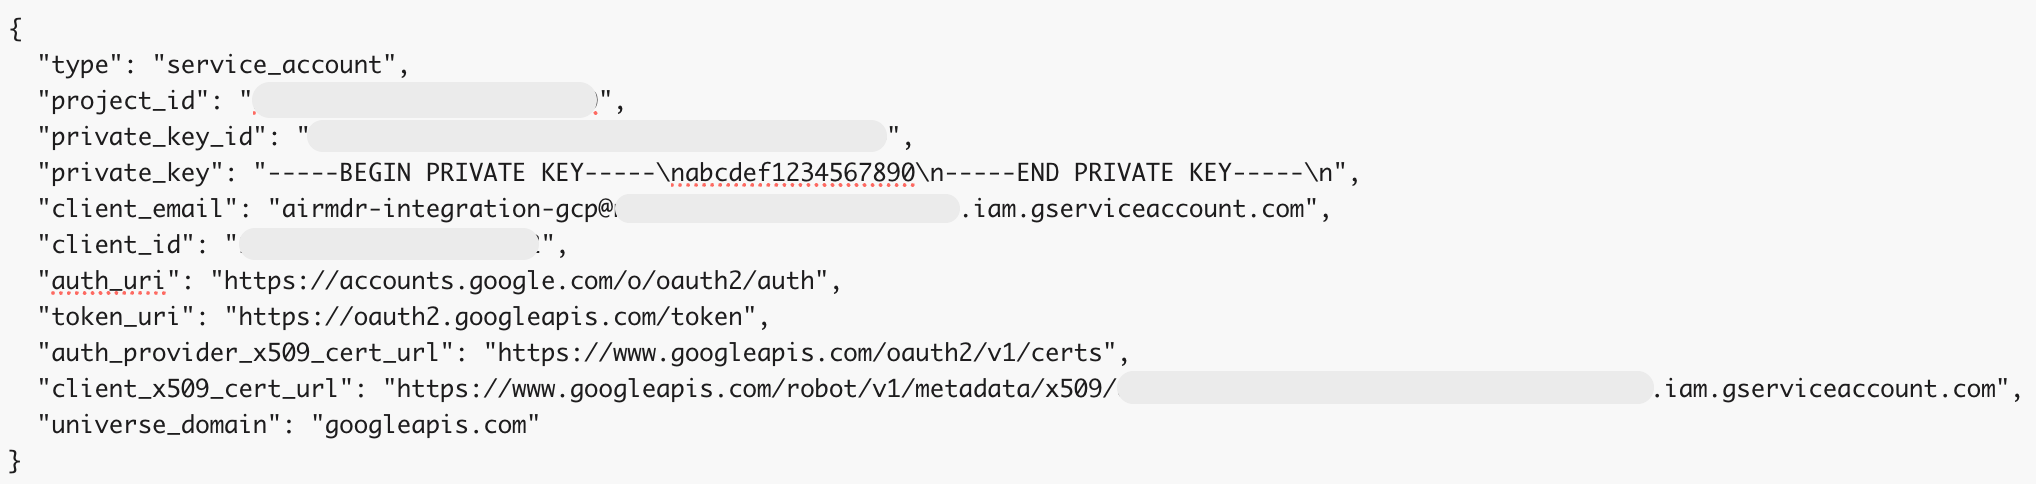 Store the JSON key securely. Do not share it over email, chat, or unsecured channels.
1. In [Google Cloud Console](https://console.cloud.google.com/welcome), go to **IAM & Admin**.
2. Select **IAM**.
Make sure the correct organization is selected.
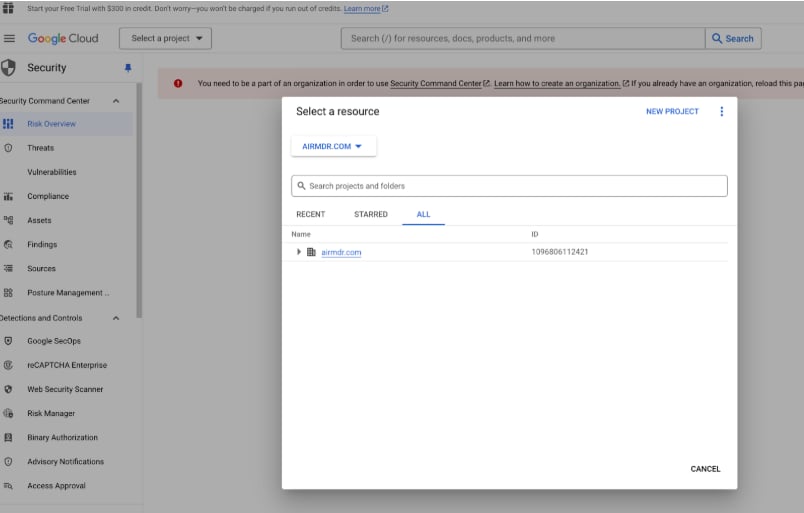 3. Click **Grant Access**.
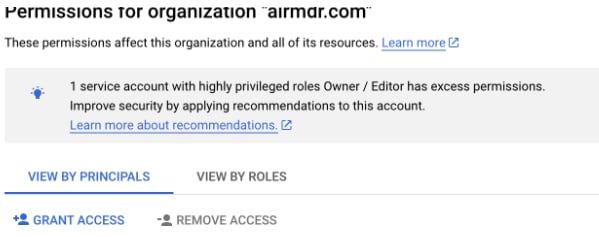 4. In **Add Principals → New principals**, enter the service account email.
Example: [airmdr-integration-gcp@example-project.iam.gserviceaccount.com](mailto:airmdr-integration-gcp@example-project.iam.gserviceaccount.com)
5. In **Assign Roles → Select a role**, search for and select:
* **Security Center Findings Viewer (**`roles/securitycenter.viewer`**)** → Grants read access
Make sure the correct Organisation is selected under **Resource**.
For example: [airmdr.com](http://airmdr.com) (Reference only as shown below)
6. Skills and Required IAM Roles
| AirMDR skill | Purpose | Required Google Cloud role | Role ID | Access | Recommended scope |
| :- | :- | :- | :- | :- | :- |
| Get GCP security command center findings | Retrieves Security Command Center findings | Security Center Findings Viewer | `roles/securitycenter.findingsViewer` | Read-only | Organization |
| Get GCP Logs | Retrieves Google Cloud logs | Logs Viewer | `roles/logging.viewer` | Read-only | Target projects or organization |
| Get GCP Configuration Changes | Retrieves configuration-change events from Cloud Logging | Logs Viewer | `roles/logging.viewer` | Read-only | Target projects or organization |
| Get GCP GKE Workload Metrics | Retrieves GKE workload metrics from Cloud Monitoring | Monitoring Viewer | `roles/monitoring.viewer` | Read-only | Target projects or organization |
| Search GCP Assets | Searches Google Cloud resource metadata | Cloud Asset Viewer | `roles/cloudasset.viewer` | Read-only | Organization |
| Search GCP IAM Policies | Searches IAM policies associated with Google Cloud resources | Cloud Asset Viewer | `roles/cloudasset.viewer` | Read-only | Organization |
| Analyze GCP IAM Policy | Analyzes IAM relationships and access policies | Cloud Asset Viewer | `roles/cloudasset.viewer` | Read-only | Organization |
| Get GCP Compute Instance | Retrieves Compute Engine instance information | Compute Viewer | `roles/compute.viewer` | Read-only | Target projects or organization |
| Get GCP Instance Effective Firewalls | Retrieves effective firewall rules for an instance | Compute Viewer | `roles/compute.viewer` | Read-only | Target projects or organization |
| Get GCP Cloud Armor Policy | Retrieves Cloud Armor security-policy information | Compute Viewer | `roles/compute.viewer` | Read-only | Target projects or organization |
| List GCP Service Account Keys | Lists service-account key metadata | Security Reviewer | `roles/iam.securityReviewer` | Read-only | Target projects or organization |
| Get GCP Org Policy | Retrieves organization-policy configuration | Organization Policy Viewer | `roles/orgpolicy.policyViewer` | Read-only | Organization |
| Get GCP IAM Recommendations | Retrieves IAM recommendations and insights | IAM Recommender Viewer | `roles/recommender.iamViewer` | Read-only | Target projects or organization |
| List GCP Container Vulnerabilities | Retrieves Container Analysis occurrence and vulnerability information | Container Analysis Occurrences Viewer | `roles/containeranalysis.occurrences.viewer` | Read-only | Target projects or organization |
| List GCP VPC SC Perimeters | Retrieves VPC Service Controls perimeter configuration | Access Context Manager Reader | `roles/accesscontextmanager.policyReader` | Read-only | Organization access policy |
To view the details of Input Parameters and Output for the respective skills
* Go to [AirMDR → Google Cloud Provider](https://app.airmdr.com/integrationsv2/be2de942-b131-4612-b944-a8631b2cba14/skills?search=google+clo) Integration page.
* Select the **Skills** tab and click on the required listed skill
7. Click **Save**.
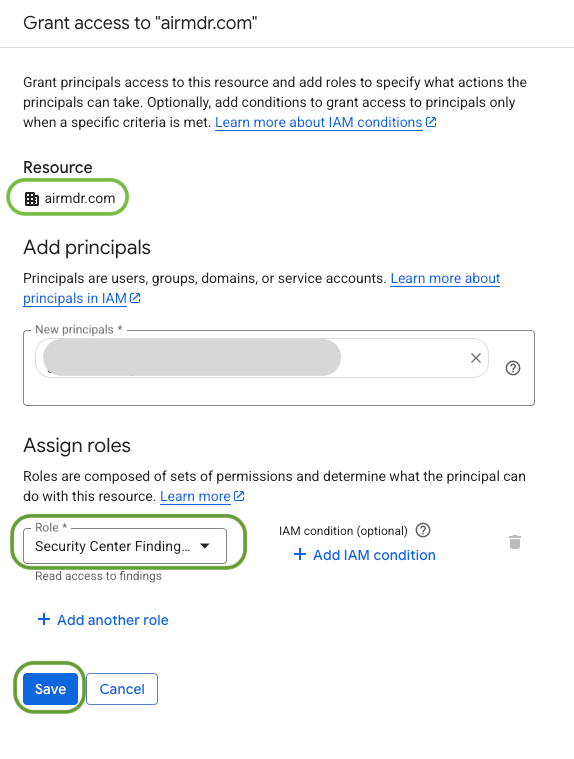 When finished, you should have a service account named **airmdr-agent**, credentials for this service account in a JSON file saved to your host.
1. In [Google Cloud Console](https://console.cloud.google.com/welcome), open the project selector at the top.
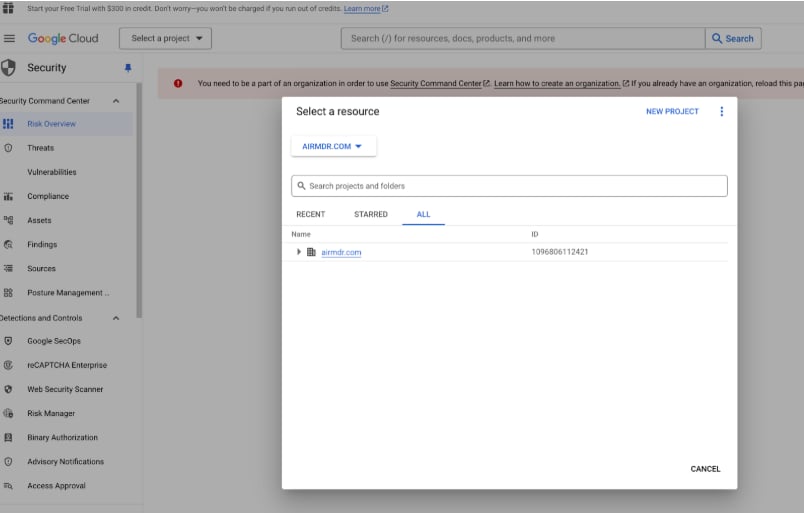 2. Select the required organization.
3. Click the three-dot menu or **More** option.
4. Select **Settings**.
5. Locate the **Organization ID** field.
6. Copy the numeric organization ID.
Example: **123456789012**
This value is the `organization_id` required in AirMDR.
### Configure GCP Security Command Center API in AirMDR Integrations Dashboard
1. Navigate to [AirMDR](https://app.airmdr.com/auth/login), provide the credentials and click **Login**
2. Navigate to the AirMDR Integrations Dashboard in the left navigation pane and select **Integrations**.
3. Use the search option, enter the keyword "**Google Cloud Provider**", select the **Connections** tab, and click **+ Create** button.
4. Enter an unique name to the Instance (e.g., `your org name-GCP`) to easily identify the user connection by AirMDR.
5. Enter the application credentials like **Service\_account\_json** and **Organization\_id** in the Authentication Details field params, and click **Save**.
### Additional Information
| **Error** | **Possible Cause** | **Recovery Step** |
| :- | :- | :- |
| Invalid service account JSON | JSON file is incomplete, modified, or incorrectly pasted. | Download a new JSON key and update the AirMDR connection. |
| Permission denied | Required IAM role is missing. | Assign Security Center Findings Viewer role to the service account. |
| Organization not found | Incorrect organization ID entered. | Recheck the organization ID from Google Cloud Console. |
| API not enabled | Security Command Center API is disabled. | Enable the Security Command Center API from APIs & Services. |
| No findings available | SCC is not enabled or there are no findings for the selected scope. | Confirm SCC activation and findings availability in Google Cloud. |
| Authentication failed | Service account key is revoked or expired. | Generate a new key and update the integration. |
***
**Where to Monitor**
| Location | What to Check |
| :- | :- |
| AirMDR Integration Page | Connection status and validation result |
| AirMDR Logs | Authentication, API, and ingestion errors |
| Google Cloud IAM Audit Logs | Service account access and permission events |
| Google Cloud API Metrics | Security Command Center API usage |
**Sample Success Log**
```text theme={null}
INFO GCP_SCC_CONNECTOR Authentication successful for organization_id=123456789012
INFO GCP_SCC_CONNECTOR Retrieved Security Command Center findings successfully
```
**Sample Error Log**
```text theme={null}
ERROR GCP_SCC_CONNECTOR Permission denied while accessing Security Command Center findings
ERROR GCP_SCC_CONNECTOR Invalid service account JSON or malformed private key
```
**Recommended Log Levels**
| Log Level | Usage |
| :- | :- |
| INFO | Successful authentication and data retrieval |
| WARN | Partial data retrieval or delayed API response |
| ERROR | Authentication failure, permission issue, invalid organization ID, or API failure |
Follow these recommendations to maintain a secure and compliant Google Cloud Security Command Center (GCP SCC) integration with AirMDR.
**✅ Do**
* Use a dedicated Service Account for the AirMDR integration.
* Grant only the minimum IAM permissions required (principle of least privilege).
* Store the Service Account JSON securely in an encrypted secrets manager or credential vault.
* Rotate Service Account keys periodically according to your organization's security policy.
* Enable Multi-Factor Authentication (MFA) for privileged Google Cloud accounts.
* Regularly review IAM roles and remove unnecessary permissions.
* Monitor Google Cloud Audit Logs for authentication and permission changes.
* Validate the integration after updating IAM roles or rotating credentials.
* Keep the Security Command Center API enabled and accessible.
* Immediately revoke compromised or unused Service Account keys.
**❌ Don't**
* Don't share the Service Account JSON file over email, chat, or unsecured channels.
* Don't commit Service Account keys to source code repositories.
* Don't assign excessive permissions such as **Owner** or **Editor** unless absolutely necessary.
* Don't reuse the same Service Account across multiple unrelated applications.
* Don't leave unused Service Account keys active.
* Don't disable audit logging for Service Account activities.
* Don't expose Organization IDs or sensitive credentials in public documentation or screenshots.
* Don't hardcode credentials in scripts or configuration files.
* Don't ignore authentication or permission-related errors during integration validation.
* Don't skip periodic access reviews and credential rotation.
* 📧 Contact [**AirMDR Support**](mailto:support@airmdr.com) through your designated support channel.
* 🔁 Rotate credentials regularly.
* 🔄 Reconnect in AirMDR when secrets are changed.
**Data Exchanged**
| Data Type | Description |
| :- | :- |
| Security findings | Findings generated by Google Cloud Security Command Center. |
| Organization metadata | Organization-level identifier used to scope the integration. |
| Authentication token | Token generated using the service account JSON. |
**Security Considerations**
* Authentication is performed using a Google Cloud service account.
* API communication uses Google Cloud HTTPS endpoints.
* Store the service account JSON securely.
* Rotate the JSON key based on the organization’s credential rotation policy.
* Revoke unused keys immediately.
**Ports and Endpoints**
| Type | Value |
| :- | :- |
| Protocol | HTTPS |
| Port | 443 |
| API Endpoint | `https://securitycenter.googleapis.com` |
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.